

Age Validation Pro - Age verification and blocking of restricted products
Verify your customers' age with a real rule engine: entry gate, product badge and genuine server-side blocking of the cart and checkout for products subject to an age limit — alcohol, tobacco, vaping, CBD, adult content. GDPR consent log and cryptographically signed cookie. Without modifying any native PrestaShop table.


Descrizione
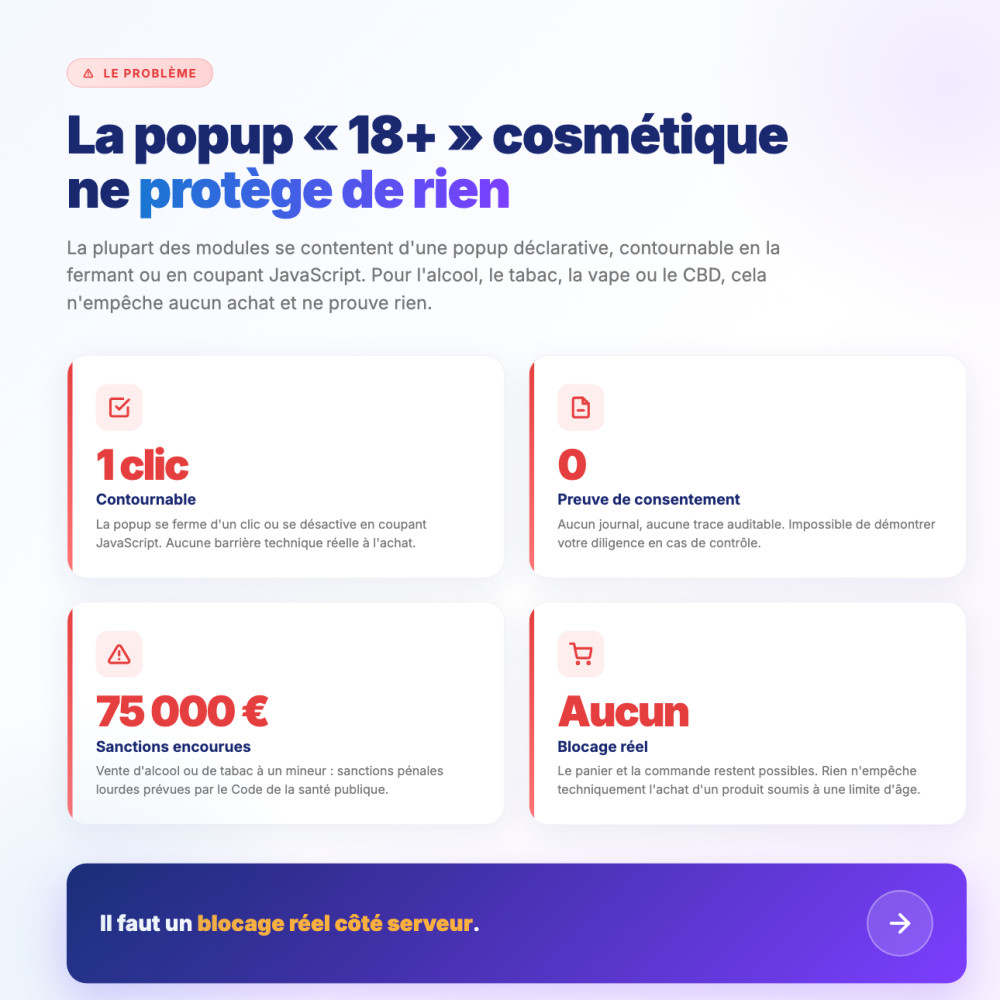
The problem
Most age verification modules settle for a declarative "18+" popup, bypassable by closing it or disabling JavaScript, with no evidential value whatsoever. At the other end, document-based verification solutions — ID, selfie — are heavy and costly.
The result: either illusory protection that commits to nothing legally, or a purchase journey so cumbersome that it drives customers away.
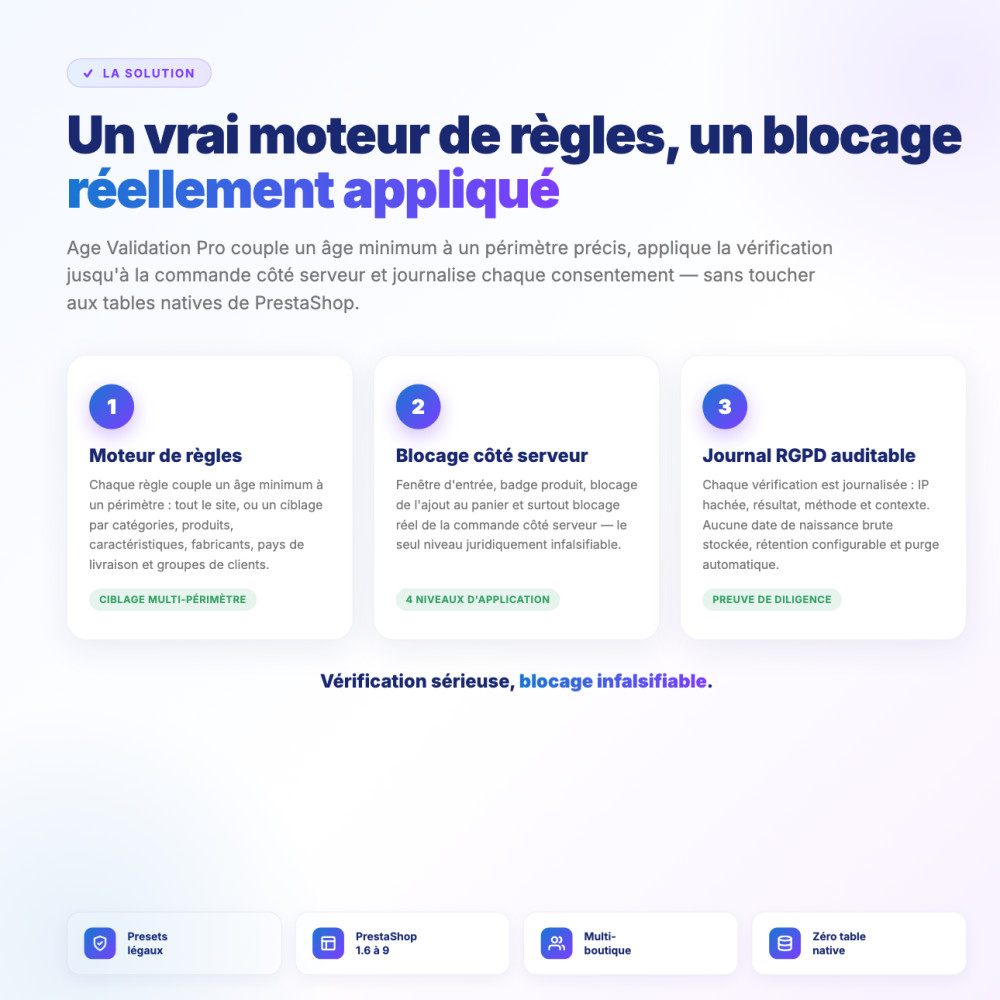
The solution
Age Validation Pro strikes the right balance: serious declarative verification — date of birth, reuse of the customer account's date of birth — paired with blocking genuinely enforced server-side for the cart and checkout, the only legally reliable level, and with an auditable consent log. All driven by a multi-scope rule engine, from PrestaShop 1.6 to 9.
How it works
Create a rule
Start from a regulatory preset (alcohol, tobacco, vaping, CBD, adult) or a blank rule: the minimum age, the mode and a standard legal message are pre-filled.
Target the scope
Apply the rule to the whole site or target categories, products, features, manufacturers, delivery countries or customer groups.
Choose the enforcement
Enable the entry gate, the product badge, the cart blocking and the server-side order blocking, then activate the rule: verification applies immediately.
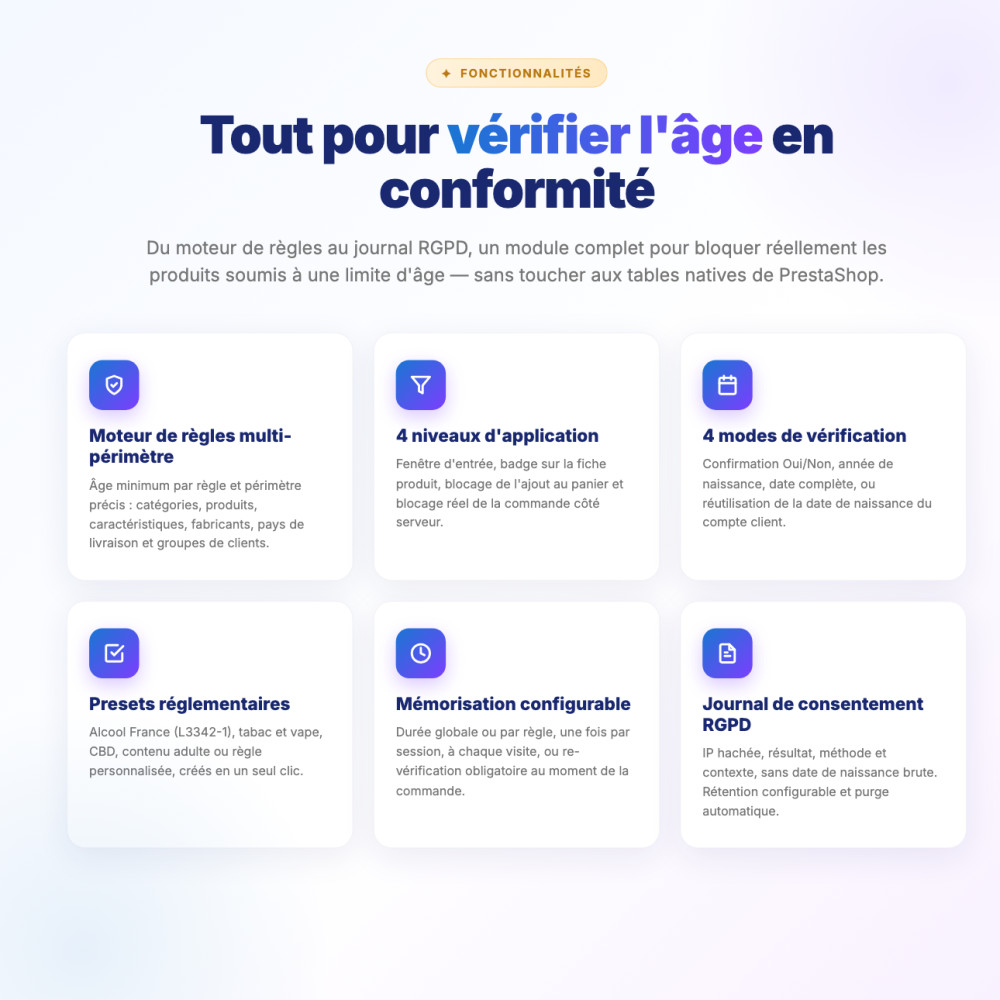
Detailed features
Multi-scope rule engine
- Minimum age configurable per rule (18, 21…)
- Targeting by categories, products, features, manufacturers, delivery countries, customer groups
- Forcing or excluding specific products
- Evaluation priority between rules
4 stackable enforcement levels
- Entry gate (full-screen overlay)
- Age badge on the product page
- Blocking of the add-to-cart
- Server-side blocking of the order — tamper-proof
4 verification modes
- Declarative Yes/No confirmation
- Year of birth
- Full date of birth
- Reuse of the customer account's date of birth
Regulatory presets
- France alcohol (art. L3342-1 of the Public Health Code)
- Tobacco and vaping
- CBD
- Adult content
- Custom rule
Configurable memorization
- Default global duration, custom duration per rule
- Once per session or on every visit
- Mandatory re-verification at checkout
GDPR consent log
- Hashed IP, result, method, context, item concerned
- No raw date of birth stored
- Configurable retention and automatic purging
- Clickable links to the product or the order
Signed cookie re-checked server-side
- Proof of age stored in a signed cookie (HMAC)
- Tamper-proof, impossible to forge client-side
- Re-checked server-side at the cart and at checkout
Gate customization
- Adjustable background and text colors
- Legal message defined per rule
- Redirect URL when verification fails
Multistore
- Compatible with PrestaShop multistore configurations
- Rules and settings managed per context
Zero native table modified
- All data in dedicated tables
- No native class override — no conflict possible
- Clean and complete uninstallation
Responsible security policy
A module adhering to the TouchWeb Charter for responsible cybersecurity: acknowledgement within 7 days for any relevant report, fix and CVE publication within 30 days, never a silent patch. AFL 3.0 license — open, auditable and modifiable code. Published by Mediacom87, PrestaShop specialist since 2008.
Installation in 4 steps
Download the module and install it from your back office (Modules > Module Manager).
Set the general settings: default minimum age, global memorization duration and gate colors.
Create your first rule from a regulatory preset (alcohol, tobacco, vaping, CBD, adult) or a blank rule, then choose the scope and the enforcement levels (gate, badge, cart, order).
Activate the rule — verification applies immediately in the front office — then review the consent log to audit the verifications.
Caratteristiche
- Minimum age configurable per rule (18, 21…)
- Targeting by categories, products, features, manufacturers, delivery countries, customer groups
- Forcing or excluding specific products
- Evaluation priority between rules
- Entry gate (full-screen overlay)
- Age badge on the product page
- Blocking of the add-to-cart
- Server-side blocking of the order — tamper-proof
- Declarative Yes/No confirmation
- Year of birth
- Full date of birth
- Reuse of the customer account's date of birth
- France alcohol (art. L3342-1 of the Public Health Code)
- Tobacco and vaping
- CBD
- Adult content
- Custom rule
- Default global duration, custom duration per rule
- Once per session or on every visit
- Mandatory re-verification at checkout
- Hashed IP, result, method, context, item concerned
- No raw date of birth stored
- Configurable retention and automatic purging
- Clickable links to the product or the order
- Proof of age stored in a signed cookie (HMAC)
- Tamper-proof, impossible to forge client-side
- Re-checked server-side at the cart and at checkout
- Adjustable background and text colors
- Legal message defined per rule
- Redirect URL when verification fails
- Compatible with PrestaShop multistore configurations
- Rules and settings managed per context
- All data in dedicated tables
- No native class override — no conflict possible
- Clean and complete uninstallation
Cronologia versioni
v1.0.0
- First public release: configurable rules engine with real server-side cart and checkout blocking.
- Legal presets (alcohol, tobacco and vaping, CBD, adult content), auditable GDPR consent log, multi-scope targeting and a customizable age gate.
Un progetto, una domanda, un audit?
Risposta personale entro 24h lavorative. Confrontiamoci senza impegno.
Parliamo del tuo progetto →